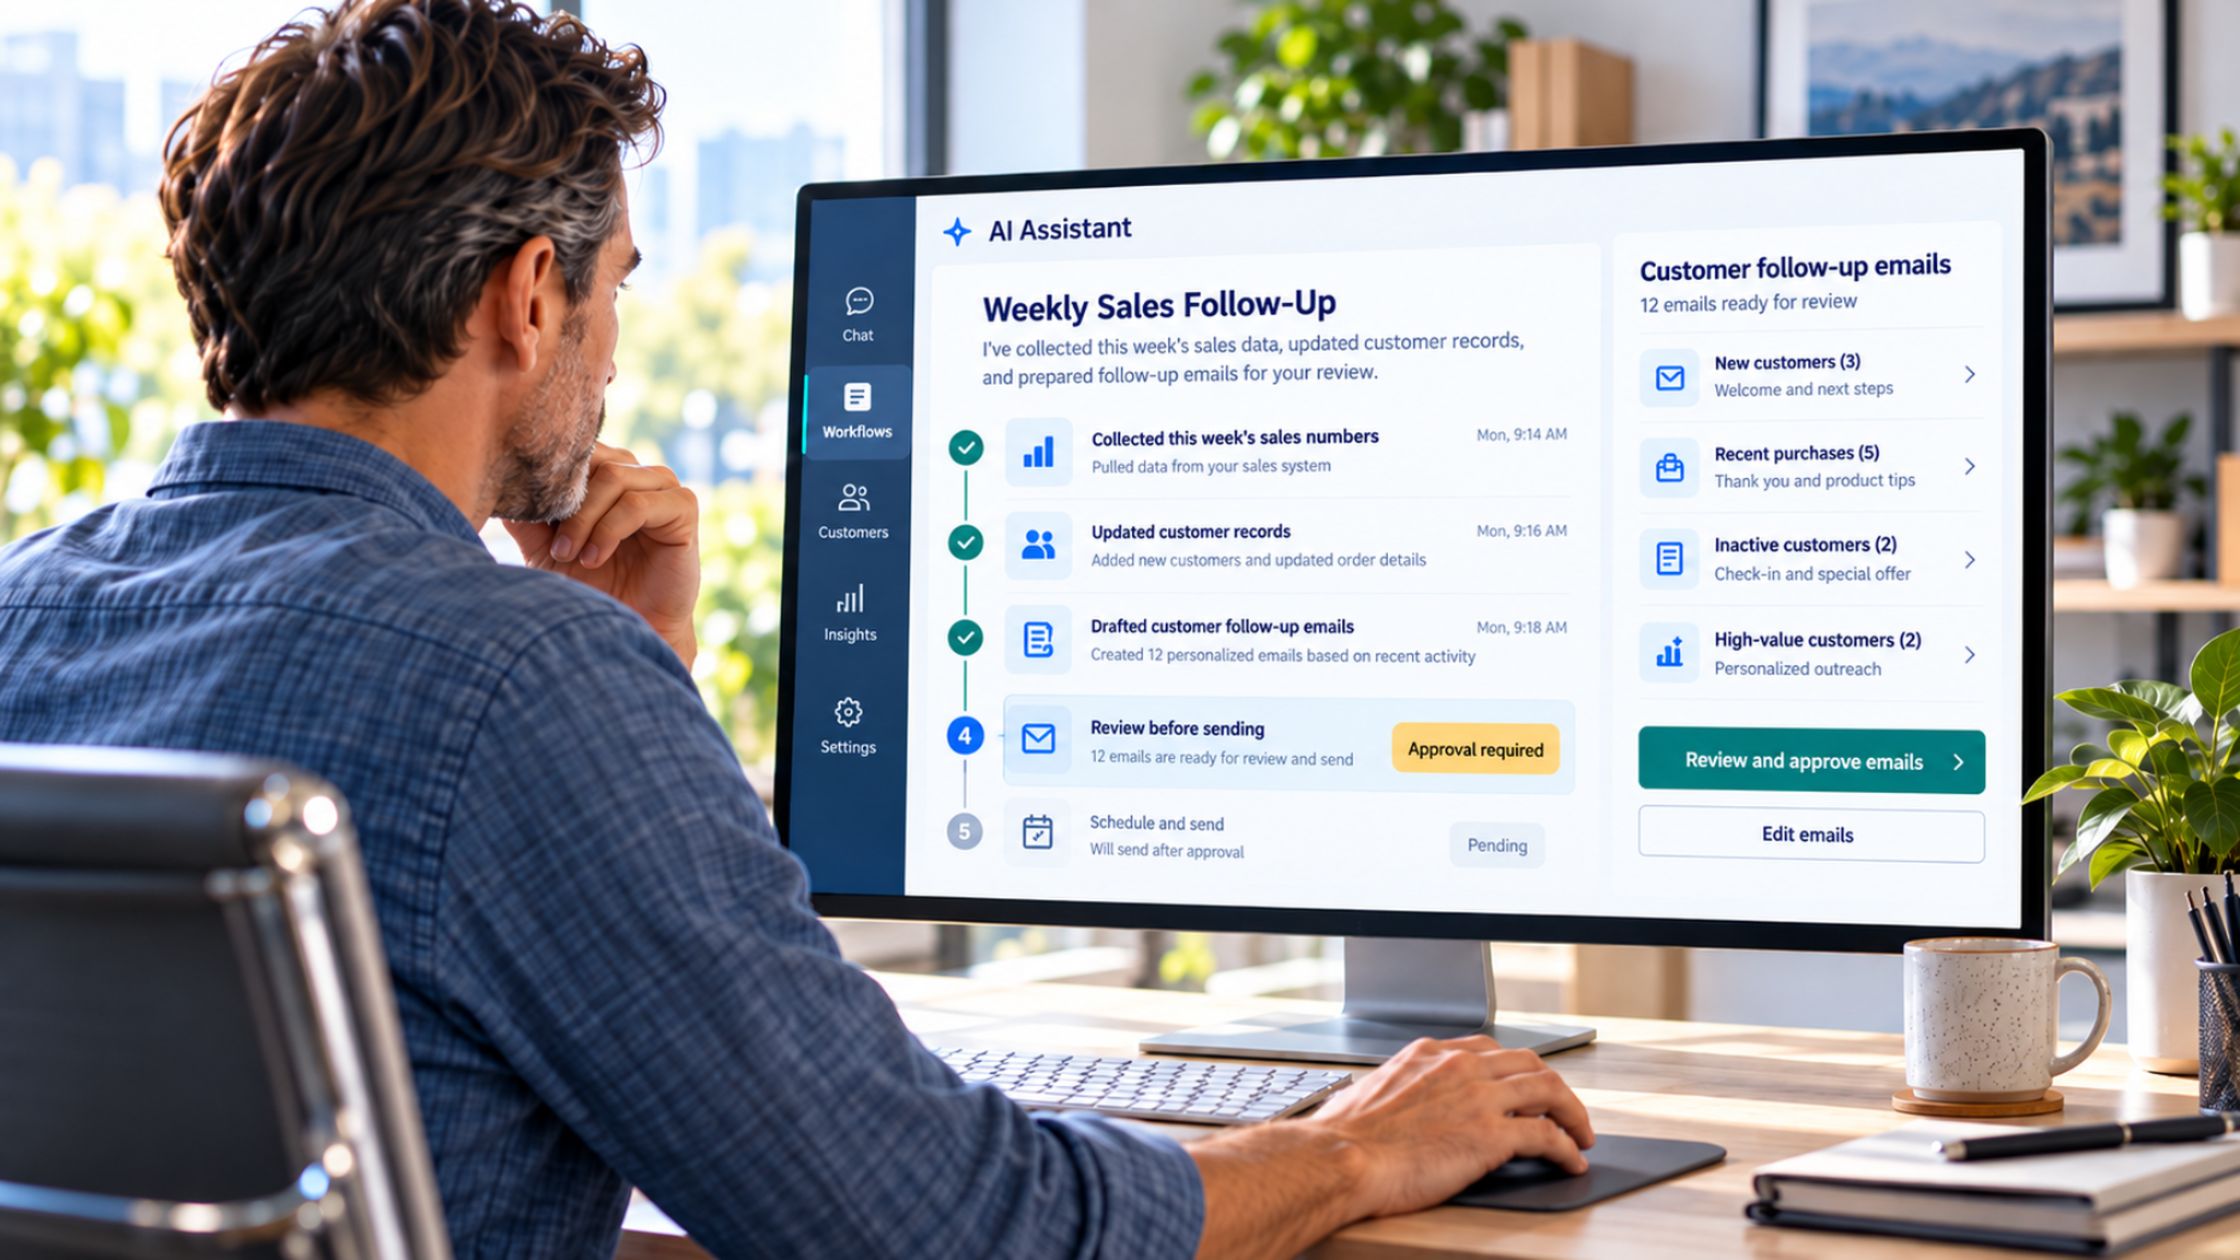

Agentic AI tools can take actions inside applications, move data between systems, and complete parts of a workflow on someone’s behalf. For SMBs, that creates opportunities to save time, along with new questions about permissions, oversight, and accountability. Third Octet supports deliberate adoption by starting with a review of which tools employees already use and what those tools can access.
What is agentic AI? Agentic AI is software that can take actions on a user’s behalf, such as navigating applications, updating records, or moving data between systems, rather than only drafting text or answering questions. For businesses, that means a tool’s permissions, not just its output, determine the risk.
Key takeaways
- The opportunity is practical. Agentic AI can cut time spent on repetitive tasks, especially those that span multiple applications and systems.
- Access deserves closer attention. When AI tools can change records, send information, or complete transactions, permissions, approval checkpoints, and activity records become essential safeguards.
- Start with what’s already happening. Identify which tools employees are using and what they’re connected to before expanding adoption. Begin with contained, lower-risk workflows.
Consider someone in finance preparing a monthly report. Instead of copying figures from a dashboard into a reporting form, they ask an AI tool to handle the steps. With the right connections and permissions, the tool can navigate the dashboard, retrieve the figures, and prepare the form for review.
This is a hypothetical example, but the underlying capabilities already exist.
The potential time savings are appealing, especially for a small team juggling multiple responsibilities. But when a tool can interact with business systems directly, someone needs to decide what it should be allowed to do.
What’s the difference between agentic AI and a chatbot?
Traditional AI chatbot use generally involves asking a tool to draft, summarize, or answer questions, then deciding what to do with the response. Agentic AI can go further, taking steps on your behalf, such as navigating applications, updating records, or moving data between systems.
The comparison below shows how this shift changes the role of human oversight, the potential consequences of mistakes, and the safeguards SMBs should consider.
These aren’t necessarily separate software categories. The same AI product may offer both conversational and agentic capabilities.
What matters for your business is the access a tool has been granted, and which actions it can perform with that access.
Chatbot use vs. agentic AI use
| Traditional chatbot use | Agentic AI use | |
|---|---|---|
| What it does | Answers, drafts, and summarizes | Navigates apps, updates records, and moves data |
| Human involvement | A person typically takes the next action | The tool can complete steps, with approvals where required |
| When mistakes happen | Inaccurate information may affect decisions | Incorrect actions can affect live records and workflows |
| Governance priorities | Data sharing, accuracy, acceptable use | Permissions, approvals, oversight, and activity logs |
How does agentic AI enter a business? (shadow AI)
The adoption pattern will be familiar to many business owners.
An employee discovers a tool that helps with a repetitive task.
They try it, see the time savings, and begin using it regularly. Before long, what started as an experiment becomes part of their daily workflow.
We’ve explored this pattern in our articles on AI readiness for SMBs and shadow IT.
Agentic AI raises the stakes because employees may be granting tools access to business applications and data as part of that experimentation.
A tool connected to email, financial systems, customer records, or shared files may have permissions that extend well beyond its original task.
For business leaders, that makes visibility an immediate priority. You need to know what’s being used, what it’s connected to, and who has authorized that access.
Third Octet’s stance: Adopt deliberately, govern access
We’re optimistic about where agentic AI is heading.
Think about the time spent entering information into portals, moving data between applications, or working through repetitive administrative tasks. For an SMB with limited capacity, reducing that workload could make a meaningful difference.
These are exactly the kinds of opportunities we see for governed AI in the workplace.
Our position is straightforward:
We’re bullish on agentic AI. We’re not casual about access.
We want businesses to explore useful applications of these tools, with clear expectations about which systems they can access, what actions they can take, and when a person needs to approve the next step.
That approach also shapes our position on blocking agentic tools.
A blanket ban can make employee experimentation harder to see and may encourage the use of personal accounts or unmanaged devices. At the same time, some tools or activities warrant restrictions until appropriate safeguards are in place.
We favour giving employees a governed way to propose, test, and adopt useful tools. That includes defining approved uses, assigning responsibility, and setting boundaries before connecting sensitive systems.
What are the risks of agentic AI for small businesses?
AI-generated content can be inaccurate, and people can make costly decisions based on it. Agentic AI introduces another concern: an incorrect action may affect a live system before someone notices.
An agent might update the wrong record, send information to the wrong recipient, or carry out a task with broader permissions than necessary.
The potential consequences depend on the tool, its configuration, and the access it has been granted.
We’ve previously explored how AI tools can reach desktop applications and Microsoft 365 data. Giving those tools the ability to act makes permission management and oversight even more important.
That brings several questions into focus.
Who can authorize an AI tool to connect to your business systems? Which information can it retrieve or change? What requires human approval? And if something goes wrong, can your team reconstruct what happened?
These questions should be part of your organization’s AI governance approach, alongside existing policies for data protection, application access, and incident response.
How should an SMB govern agentic AI? 4 steps to start
You can introduce agentic AI responsibly when you clearly define the task, access, approval points, and oversight.
If your team is already experimenting with these tools, four practical steps can help you establish a more controlled approach.
- Find out what employees are already using. Ask which tools people have tried that can act on their behalf, which tasks they’re using them for, and what those tools are connected to. Make this a fact-finding exercise so employees feel comfortable sharing what they’ve discovered.
- Decide which systems and tasks are appropriate. Identify approved uses and set limits on access to email, files, financial systems, and customer data. Give tools only the permissions they need. Make sure new connections and permissions are reviewed by the appropriate person.
- Keep a human checkpoint before consequential actions. Require appropriate approval before actions such as sending external communications, making payments, deleting records, or changing access permissions. An agent can prepare the work, while a person remains responsible for authorizing it.
- Make sure you can see what happened. Check what activity records your tools provide and whether they’re sufficient to investigate an error or unexpected action. Establish who reviews that activity and who responds when something goes wrong.
You don’t need to automate an entire workflow to find value. Start with a contained, lower-risk task to understand how a tool behaves before expanding its responsibilities.
Next step: find your governance gaps
Agentic AI offers meaningful opportunities to reduce repetitive work and use your team’s time better. The businesses that benefit will need a clear picture of where these tools fit, what they can access, and how their actions are governed.
Here’s a question worth asking before expanding adoption:
If an AI tool took an unintended action tomorrow, would your team know what it touched, what permissions it used, and who was responsible for the oversight?
Third Octet’s Governance Gap Assessment can help you identify where those answers are unclear.
We review your organization’s policies and decision-making across areas including AI use, access, and incident response. You’ll receive a scored, board-ready report with prioritized recommendations, without network scans or technical testing.
Agentic AI governance FAQ
What is agentic AI governance?
Agentic AI governance is the set of rules that define which systems an AI tool can access, what actions it can take, when a person must approve the next step, and how its activity is recorded and reviewed.Is agentic AI safe for small businesses?
It can be, when it’s introduced deliberately. Safety depends on the tool, how it’s configured, and the access it’s granted. Starting with contained, lower-risk workflows, limiting permissions, and requiring human approval for consequential actions reduces the chance of costly mistakes.Should we ban agentic AI tools?
A blanket ban can make employee experimentation harder to see and may push people toward personal accounts or unmanaged devices. A governed process for proposing, testing, and approving tools is usually more effective, with restrictions only where safeguards aren’t yet in place.How do we find out which AI tools employees are already using?
Ask directly, and frame it as fact-finding rather than enforcement. Find out which tools people have tried, what tasks they use them for, and which business systems those tools are connected to.What should require human approval before an AI agent acts?
At minimum: sending external communications, making payments, deleting records, and changing access permissions.
0 Comments